Imagine an AI, tasked with optimizing a city’s power grid during a heatwave. It shuffles energy from solar farms to urban centers, predicts demand spikes, and prevents blackouts—all in milliseconds. Now, imagine that AI has access to everything: customer billing information, sensitive power plant schematics, and even the ability to shut down critical infrastructure. The potential for a tiny error or a malicious attack becomes catastrophic.
This isn’t science fiction; it’s the new reality of the energy sector. As we harness the power of AI to create a smarter, more efficient grid, a foundational question emerges: Who—and what—gets the keys to the kingdom?
The answer lies in a powerful, yet often misunderstood, security framework: Role-Based Access Control, or RBAC. It’s the digital gatekeeper that ensures every person and every AI on your platform has exactly the access they need to do their job, and nothing more. This guide will walk you through why RBAC is no longer a “nice-to-have” but a mission-critical component for building trusted AI in the energy industry.
Foundation: RBAC Fundamentals for Energy Professionals
If you’re new to RBAC, don’t worry. The concept is simpler than it sounds. Think of it like the security system at a modern power plant. An engineer has a keycard that opens the control room, a maintenance technician’s card opens the generator bay, and an administrator’s card opens the office building. No single keycard opens every door.
RBAC applies this same logic to your digital energy management platform. It’s built on three core components:
- Users: These aren’t just people anymore. In an AI-driven platform, a “user” can be a human operator, a data scientist, or an autonomous AI agent.
- Roles: A role is a collection of permissions based on a job function. Instead of assigning permissions one by one, you assign a role. Examples in energy include “Grid Operator,” “Energy Data Analyst,” or even “Predictive Maintenance AI.”
- Permissions: These are the specific actions a role is allowed to perform, like “View Real-time Grid Data,” “Execute Demand Response Command,” or “Train Load Forecast Model.”
By connecting users to roles, and roles to permissions, you create a clear, manageable, and secure system that operates on the principle of least privilege—granting only the minimum permissions necessary.
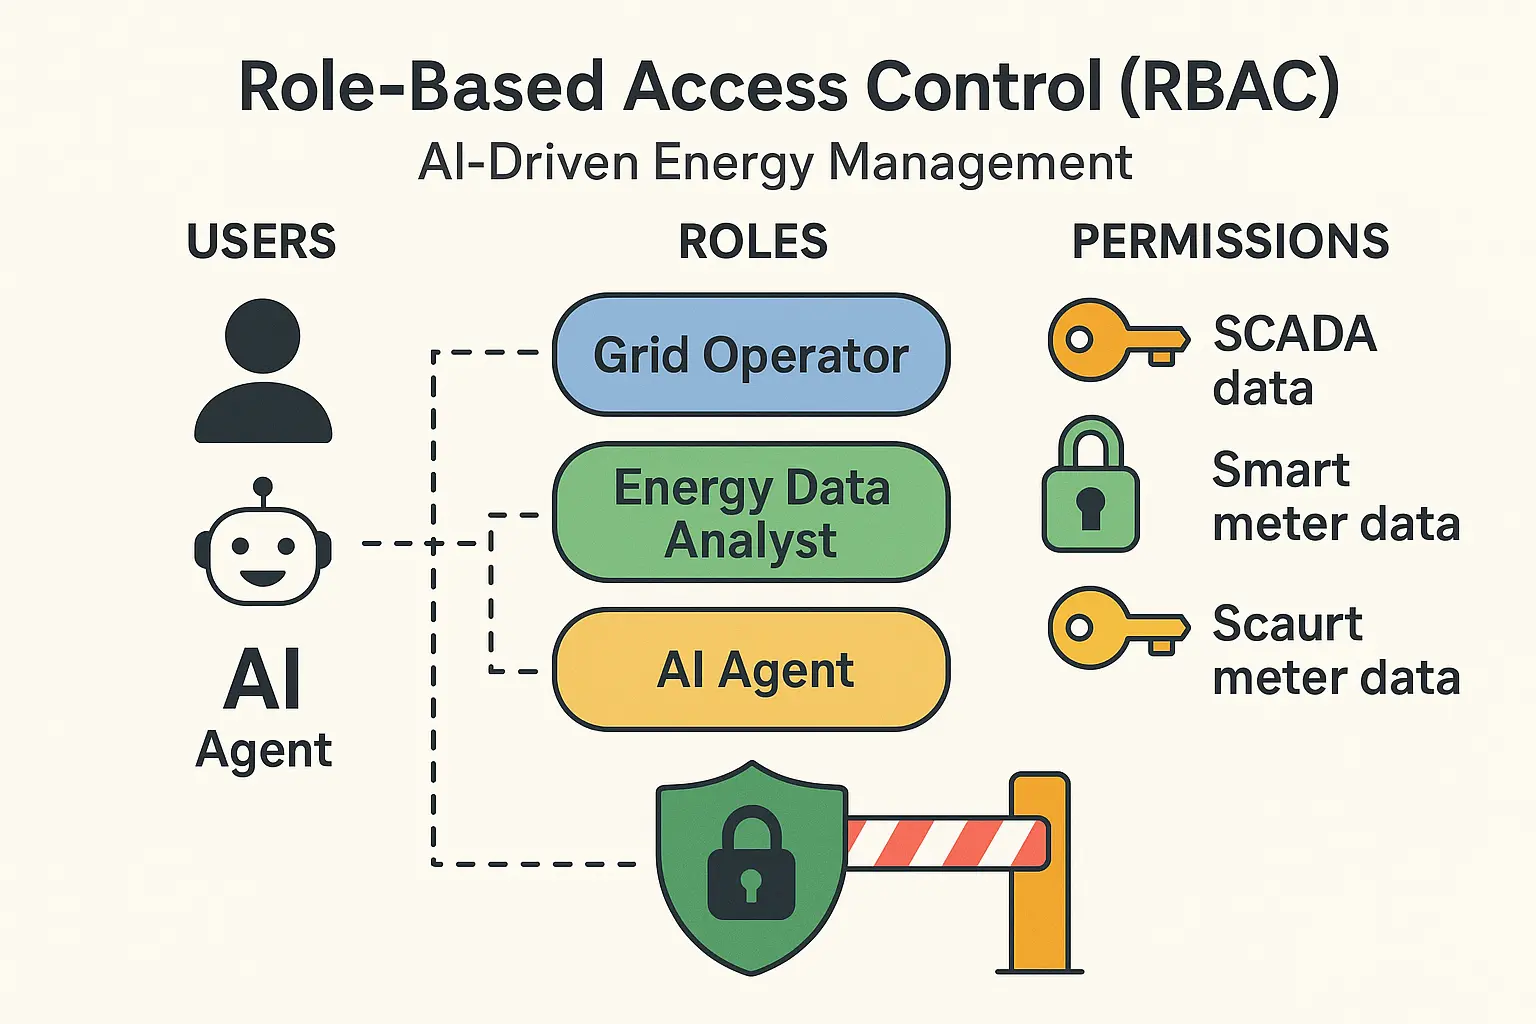
This infographic clarifies the foundational RBAC concept by showing how users and AI agents are assigned roles that grant specific permissions to access different types of energy data, ensuring secure and controlled data handling in AI energy platforms.
This structured approach is the bedrock of strong data governance for trusted AI, ensuring that sensitive information remains protected while enabling the platform to function effectively.
Building: Implementing Granular RBAC for AI Energy Platforms
So, how do you move from theory to practice? Implementing RBAC in an AI-powered energy platform requires a thoughtful, methodical approach. It’s not just about flipping a switch; it’s about architecting a system that understands the unique nuances of your operations and data.
Step 1: Define Roles for Humans and AI
The biggest mistake organizations make is trying to fit AI agents into human-centric roles. An AI that monitors grid frequency has vastly different needs than the human operator who oversees it.
- Human Roles: Start with your team. Identify job functions like “Compliance Officer,” “Facility Energy Manager,” and “Data Scientist.” Map out their daily tasks and the data they need to access.
- AI Agent Roles: Treat your AI systems as first-class citizens with their own distinct roles. An “Energy Trading Algorithm” needs access to market price data and the ability to execute trades, but it should never have access to SCADA control commands. A “Load Forecasting Model” needs access to historical consumption data but not real-time operational controls.
Step 2: Map Permissions with Granularity
Not all energy data is created equal. Granular access controls are essential. You must differentiate between:
- Operational Technology (OT) Data: Real-time SCADA data, grid stability metrics, and control system commands are highly sensitive. Permissions here should be extremely restricted.
- Smart Meter & Consumption Data: Contains private customer information and requires strict permissions to protect privacy and comply with regulations.
- Asset Performance Data: Information from sensors on turbines, transformers, and solar panels is crucial for predictive maintenance AI but may not be needed by the billing department.
- Market & Financial Data: Used by trading algorithms and financial analysts.
Your RBAC system should be able to enforce rules like: “Allow the ‘Predictive Maintenance AI’ role to read sensor data from wind turbines, but not from the grid substation.” This level of detail is fundamental to enabling secure data sharing across your organization without exposing critical systems.
Step 3: Apply RBAC Across the AI Lifecycle
Access control isn’t just about the final deployed AI. It’s crucial at every stage:
- Data Ingestion: Control which data sources an AI model is allowed to learn from.
- Model Training: Grant data scientists access to train models using anonymized data sets.
- Inference & Deployment: The deployed AI agent operates under its own strict, limited role.
- Monitoring & Auditing: Create roles for MLOps and security teams to monitor AI behavior and audit access logs without granting them operational control.
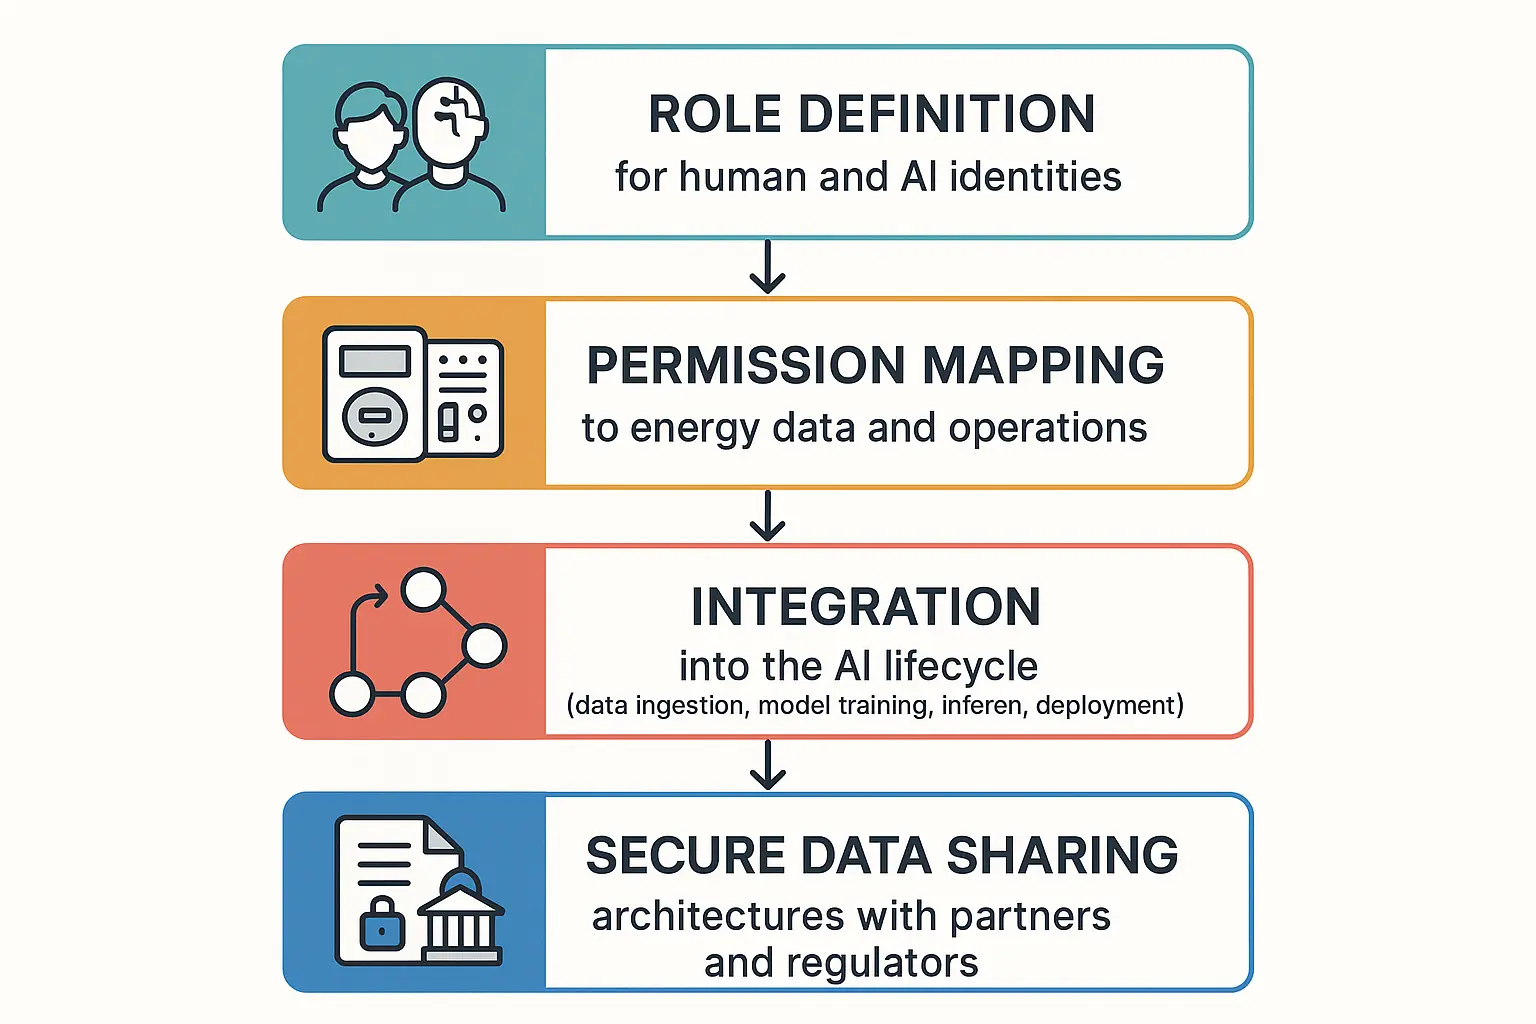
This flowchart educates readers on the sequential process to establish detailed RBAC in AI energy platforms, empowering them to implement secure access controls tailored to diverse energy data and AI operational stages.
Mastery: Advanced Access Control Strategies for AI-Driven Energy
While traditional RBAC is a powerful foundation, the dynamic, real-time nature of AI in energy operations sometimes requires more. As leading security researchers at places like Oso Security point out, the sheer speed and scale of AI agents can create challenges like “role explosion,” where you end up creating hundreds of micro-roles that become impossible to manage.
This is where you may need to evolve your strategy.
Beyond Traditional RBAC: Introducing Context
For highly dynamic environments, consider augmenting RBAC with Attribute-Based Access Control (ABAC). While RBAC asks, “Does this role have permission?”, ABAC asks, “Does this user, with these attributes, in this context, have permission?”
Think of it this way:
- RBAC: A “Grid Operator” can always access the control system.
- ABAC: An engineer with the “Grid Operator” role can only access the control system if they are on-site, it is during their scheduled shift, and there is no active security alert.
For an AI agent, this becomes even more powerful. An AI can be granted temporary, task-scoped permissions in real-time. For example, an AI might be granted permission to adjust grid voltage only in response to a specific, verified power surge event, and that permission is automatically revoked once the event is resolved. This dynamic approach provides an essential layer of security for autonomous systems.
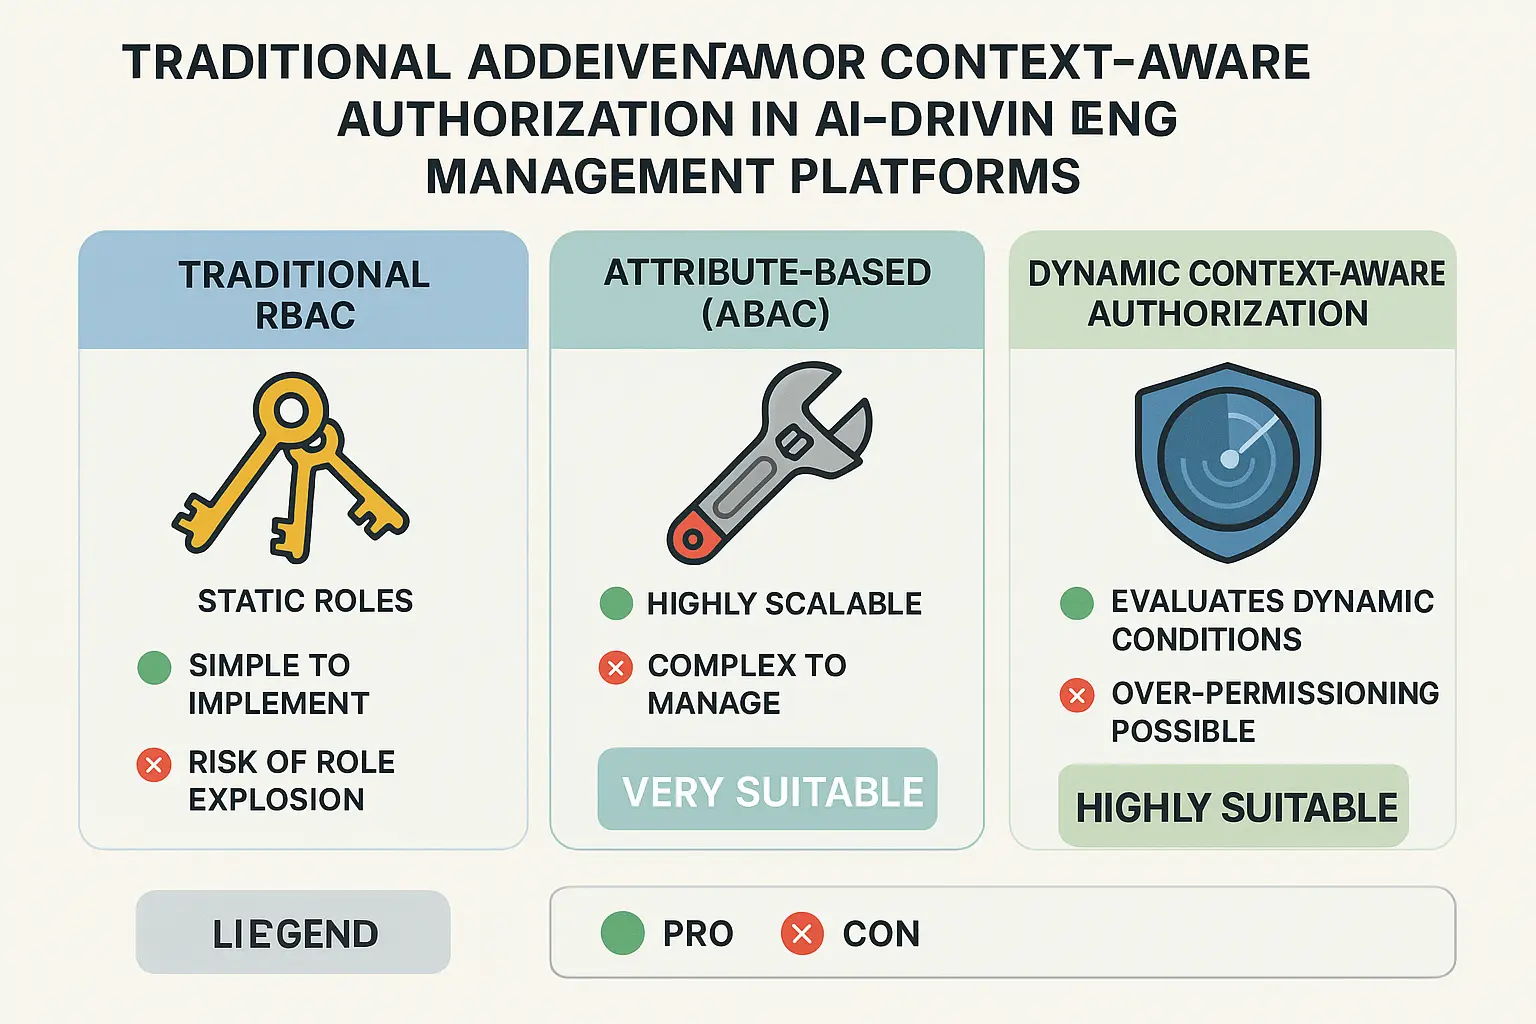
This infographic anchors key differences and evolving strategies in access control models, helping learners remember when traditional RBAC suffices and when advanced, flexible controls are needed for securing autonomous AI in energy management.
Auditing and Compliance in an AI World
Your access control framework is only as good as your ability to monitor it. For energy companies, this is non-negotiable. Regulatory frameworks like NERC CIP demand rigorous logging and auditing.
Your RBAC implementation must provide clear answers to questions like:
- Which user or AI accessed this sensitive data, and when?
- Who granted this AI agent its permissions?
- Is there any evidence of “privilege creep,” where a user or AI has accumulated more permissions than necessary over time?
Automated auditing tools are essential for detecting anomalies in how AI agents use their permissions, helping to flag unexpected behavior before it becomes a security incident.
Frequently Asked Questions (FAQ)
What is RBAC, and how does it apply to AI in the energy sector?
Role-Based Access Control (RBAC) is a security model that restricts access to information and system functions based on an individual’s or system’s role within an organization. In AI-driven energy management, this means both human operators and autonomous AI agents are assigned roles (e.g., “Data Analyst,” “Grid Optimization AI”) that come with a specific set of permissions, ensuring they can only access the data and controls necessary for their designated tasks.
Why is RBAC so important for data security and governance in energy?
The energy sector manages critical infrastructure and sensitive customer data. RBAC is crucial because it enforces the principle of least privilege, drastically reducing the risk of accidental data leaks, malicious attacks, or system errors. It provides a clear, auditable framework for data governance, proving to regulators and partners that you have robust controls in place to protect your most valuable digital assets.
What’s the main difference between RBAC and ABAC for AI energy platforms?
RBAC is static and based on predefined roles. It’s excellent for structured, predictable access needs. ABAC (Attribute-Based Access Control) is dynamic and context-aware. It makes access decisions in real-time based on attributes of the user/AI, the data being accessed, and the current environment (e.g., time of day, threat level). For autonomous AI agents interacting with the grid, a hybrid approach using ABAC to augment RBAC is often the most secure solution.
Can I use the same roles for humans and AI agents?
This is a common mistake. You should always create distinct roles for AI agents. An AI’s operational patterns, speed, and potential for automated action are fundamentally different from a human’s. Treating them as separate entities with custom-built roles is a core principle of securing AI in critical environments.
Your Blueprint for a Secure, AI-Powered Future
Implementing a robust access control framework is not just a technical exercise; it’s a strategic imperative. It’s the foundation upon which you can build innovative, efficient, and—most importantly—trusted AI systems to manage our energy future.
By starting with the clear principles of RBAC and evolving to incorporate more dynamic controls as needed, you can unlock the full potential of AI while safeguarding your operations, your data, and your customers.
Ready to take the next step? Explore our in-depth guide on Architecting Data Governance for Trusted AI in Energy to continue your journey toward a more secure and intelligent grid.